A “Your connection is not private” warning should be treated first as a certificate trust problem, not a generic Wi Fi issue. The browser is saying it cannot prove the site is who it claims to be. A network problem can cause it, but the fastest fix comes from reading the certificate error code before rebooting routers, changing DNS, or blaming the laptop.
TLDR: Browser certificate errors usually point to expired certificates, wrong system time, captive portals, antivirus inspection, or a host name mismatch. Network troubleshooting matters when many sites fail, DNS gives odd results, or public Wi Fi redirects traffic. For example, a small office with 42 laptops may find that 38 fail after a firewall SSL inspection update, while 4 work because they missed the policy change. That pattern saves hours of random resets.
What the Warning Really Means
The message “Your connection is not private” appears when a browser cannot complete a trusted HTTPS connection. Chrome may show NET::ERR_CERT_DATE_INVALID, NET::ERR_CERT_AUTHORITY_INVALID, or NET::ERR_CERT_COMMON_NAME_INVALID. Firefox, Edge, and Safari use different wording, but the meaning is similar.
HTTPS depends on certificates. A certificate links a domain name to an identity. It is signed by a trusted certificate authority. The browser checks the domain, expiry date, issuing authority, and certificate chain. If one piece fails, the browser blocks the page or shows a scary red warning.
That warning is not decoration. It protects users from fake banking pages, traffic interception, and broken server setups. Still, it can also appear because a laptop clock is wrong by five years. Annoying? Absolutely. It drives people crazy when one bad clock makes a normal site look dangerous.
Certificate Error or Network Fault?
The key question is simple: does the problem affect one site, many sites, or every secure site?
- One site fails: The website probably has a certificate issue. It may be expired, misconfigured, or issued for the wrong domain.
- Many unrelated sites fail: The device, security software, proxy, or network may be interfering with HTTPS.
- Only public Wi Fi fails: A captive portal may be blocking HTTPS until the user accepts terms on a login page.
- Only one browser fails: Browser settings, cached HSTS rules, extensions, or local certificate stores may be involved.
Good troubleshooting starts with the error code. Guessing wastes time. A router restart may help a bad DNS or captive portal problem, but it will not fix an expired certificate on a website.
Common Browser Certificate Errors
Expired certificate: The site owner forgot to renew the certificate. Browsers compare the certificate dates against the device clock. If the site certificate expired yesterday, everyone sees the warning. If the laptop thinks it is 2031, many sites may fail.
Name mismatch: The certificate was issued for one domain but used on another. For example, a certificate for www.example.com may not cover shop.example.com. This is common after site migrations or load balancer changes.
Untrusted authority: The certificate was signed by an authority the browser does not trust. This can happen with self-signed certificates, company inspection tools, school filtering systems, and poorly configured servers.
Broken certificate chain: The site certificate may be valid, but the server failed to send intermediate certificates. Some browsers fill the gap from cache. Others do not. That creates the maddening case where the site works on one computer but not another.
When the Network Is the Real Suspect
Network troubleshooting becomes more relevant when the error appears across many trusted sites. A coffee shop Wi Fi network, airport hotspot, or hotel login page may intercept first traffic. Since HTTPS resists interception, the browser may show a privacy warning instead of the login screen.
DNS can also send traffic to the wrong place. If a router uses a poisoned, stale, or filtered DNS resolver, the browser may reach a server that presents the wrong certificate. The page looks suspicious because it is suspicious, even if the user typed the right address.
Security appliances create another messy case. Many companies use HTTPS inspection to scan encrypted traffic. The appliance creates substitute certificates on the fly. This works only when every device trusts the company root certificate. If that root certificate is missing, every inspected site looks untrusted.
A Practical Triage Checklist
Support teams and careful users can cut through the noise with a short process:
- Read the exact error code. It gives the best clue.
- Check the device time and time zone. A wrong clock is a simple fix.
- Test another website. Pick a major site that normally has valid HTTPS.
- Try another network. Mobile hotspot testing can separate device issues from router issues.
- Try another browser. This can expose browser cache, extensions, or profile damage.
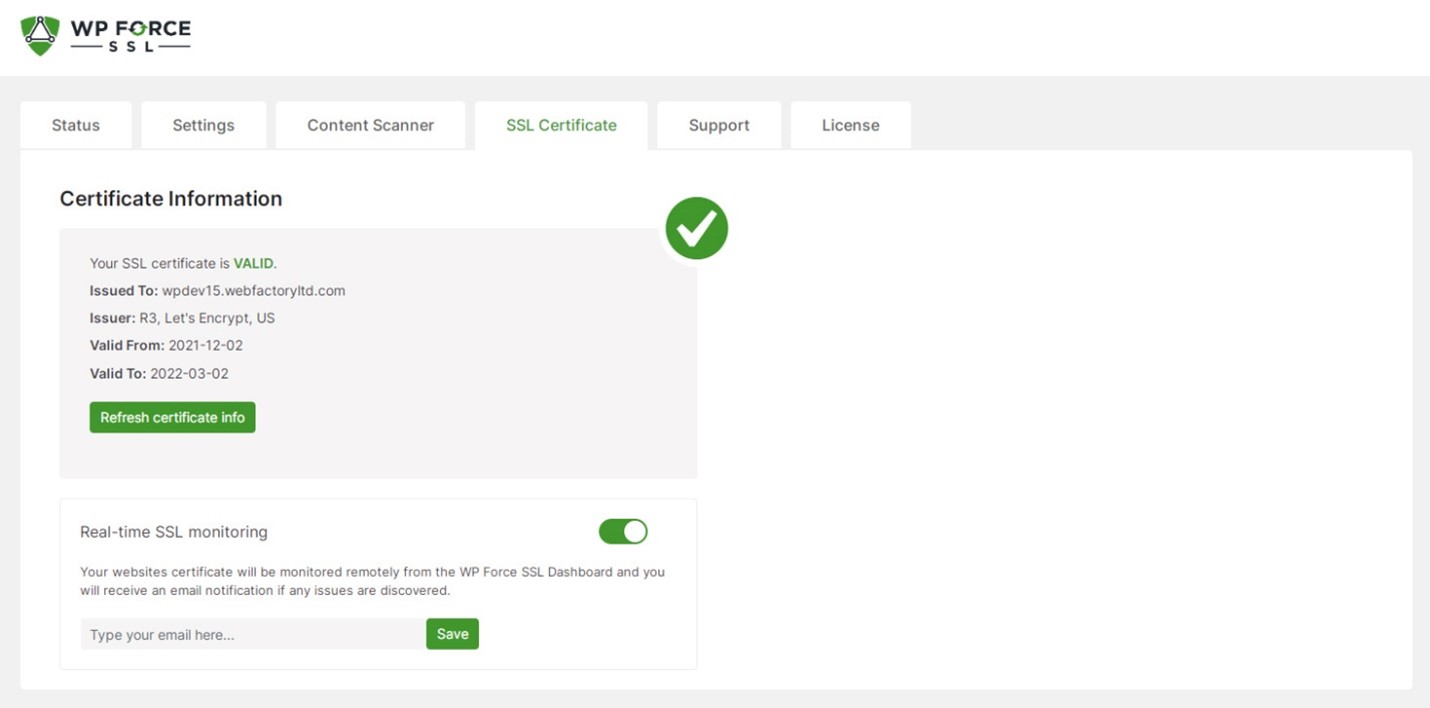
- Inspect the certificate. Look at expiry, issuer, and subject name.
- Disable HTTPS scanning briefly, if policy allows. Security software sometimes breaks trust checks.
- Flush DNS or change DNS resolver. This helps when traffic is going to the wrong server.
Expect to waste time if the error text is copied loosely. “SSL error” is too vague. NET::ERR_CERT_DATE_INVALID and SEC_ERROR_UNKNOWN_ISSUER point to very different causes.
What Users Should Not Do
Clicking through the warning is risky. Some browsers allow an advanced bypass. Others block it when HSTS is active. That is intentional. Banking, email, cloud storage, payroll, and admin panels should never be opened through a certificate warning.
Users should also avoid installing random “certificate fix” downloads. Fake fixes are a common malware path. A real fix comes from correcting time, cleaning DNS, changing network settings, updating the browser, removing a bad proxy, or asking the site owner to repair the certificate.
How Site Owners Should Respond
For a site owner, a certificate warning is urgent. Sales pages, login portals, API endpoints, and checkout pages can lose trust in seconds. Renewal automation should be monitored, not assumed. Certificate expiry alerts should fire at least 30, 14, and 7 days before expiration.
Site owners should check the full chain after every hosting move, CDN change, or domain update. They should also confirm that both root and subdomains are covered. Wildcard certificates help, but they do not cover every structure. A certificate for *.example.com does not cover api.shop.example.com.
Browser Error vs Network Troubleshooting: The Simple Rule
If one site fails, investigate the certificate first. If many trusted sites fail, inspect the device, network, DNS, proxy, and security tools. If the problem appears only on public Wi Fi, find the captive portal. If the problem appears after a firewall or antivirus update, check HTTPS inspection.
The browser warning is not the enemy. It is a signal. The skill lies in knowing whether that signal points to a broken website, an untrusted middlebox, a bad clock, or a network sending traffic where it should not go.
FAQ
What does “Your connection is not private” mean?
It means the browser cannot verify a trusted encrypted connection to the website. The certificate may be expired, invalid, mismatched, or issued by an untrusted authority.
Is it safe to continue past the warning?
Usually, no. It is especially unsafe for banking, email, shopping, work portals, and any page that asks for a password or payment details.
Can bad Wi Fi cause certificate errors?
Yes. Public Wi Fi, captive portals, DNS problems, proxies, and security filters can cause certificate warnings. Still, the error code should be checked before blaming the network.
Why does the error appear on one device only?
The device may have the wrong date, missing root certificates, different antivirus settings, a browser extension, or a proxy configuration that other devices do not use.
Why does the warning happen after antivirus installation?
Some antivirus tools inspect HTTPS traffic. If their local certificate is not trusted by the browser, secure sites may show certificate authority errors.
What is the fastest first step?
Check the exact browser error code and confirm the device time. Those two checks often separate a simple local problem from a real site or network failure.